SentriKat Early Access is open: Cloud is free on the plan you choose, no credit card. Get started

Blog

Practical guides on vulnerability management, compliance, and cybersecurity for European organizations.

PHP2Shell: the hard part is not hearing about it, it's knowing which server to fix today NIS2 ★ Latest

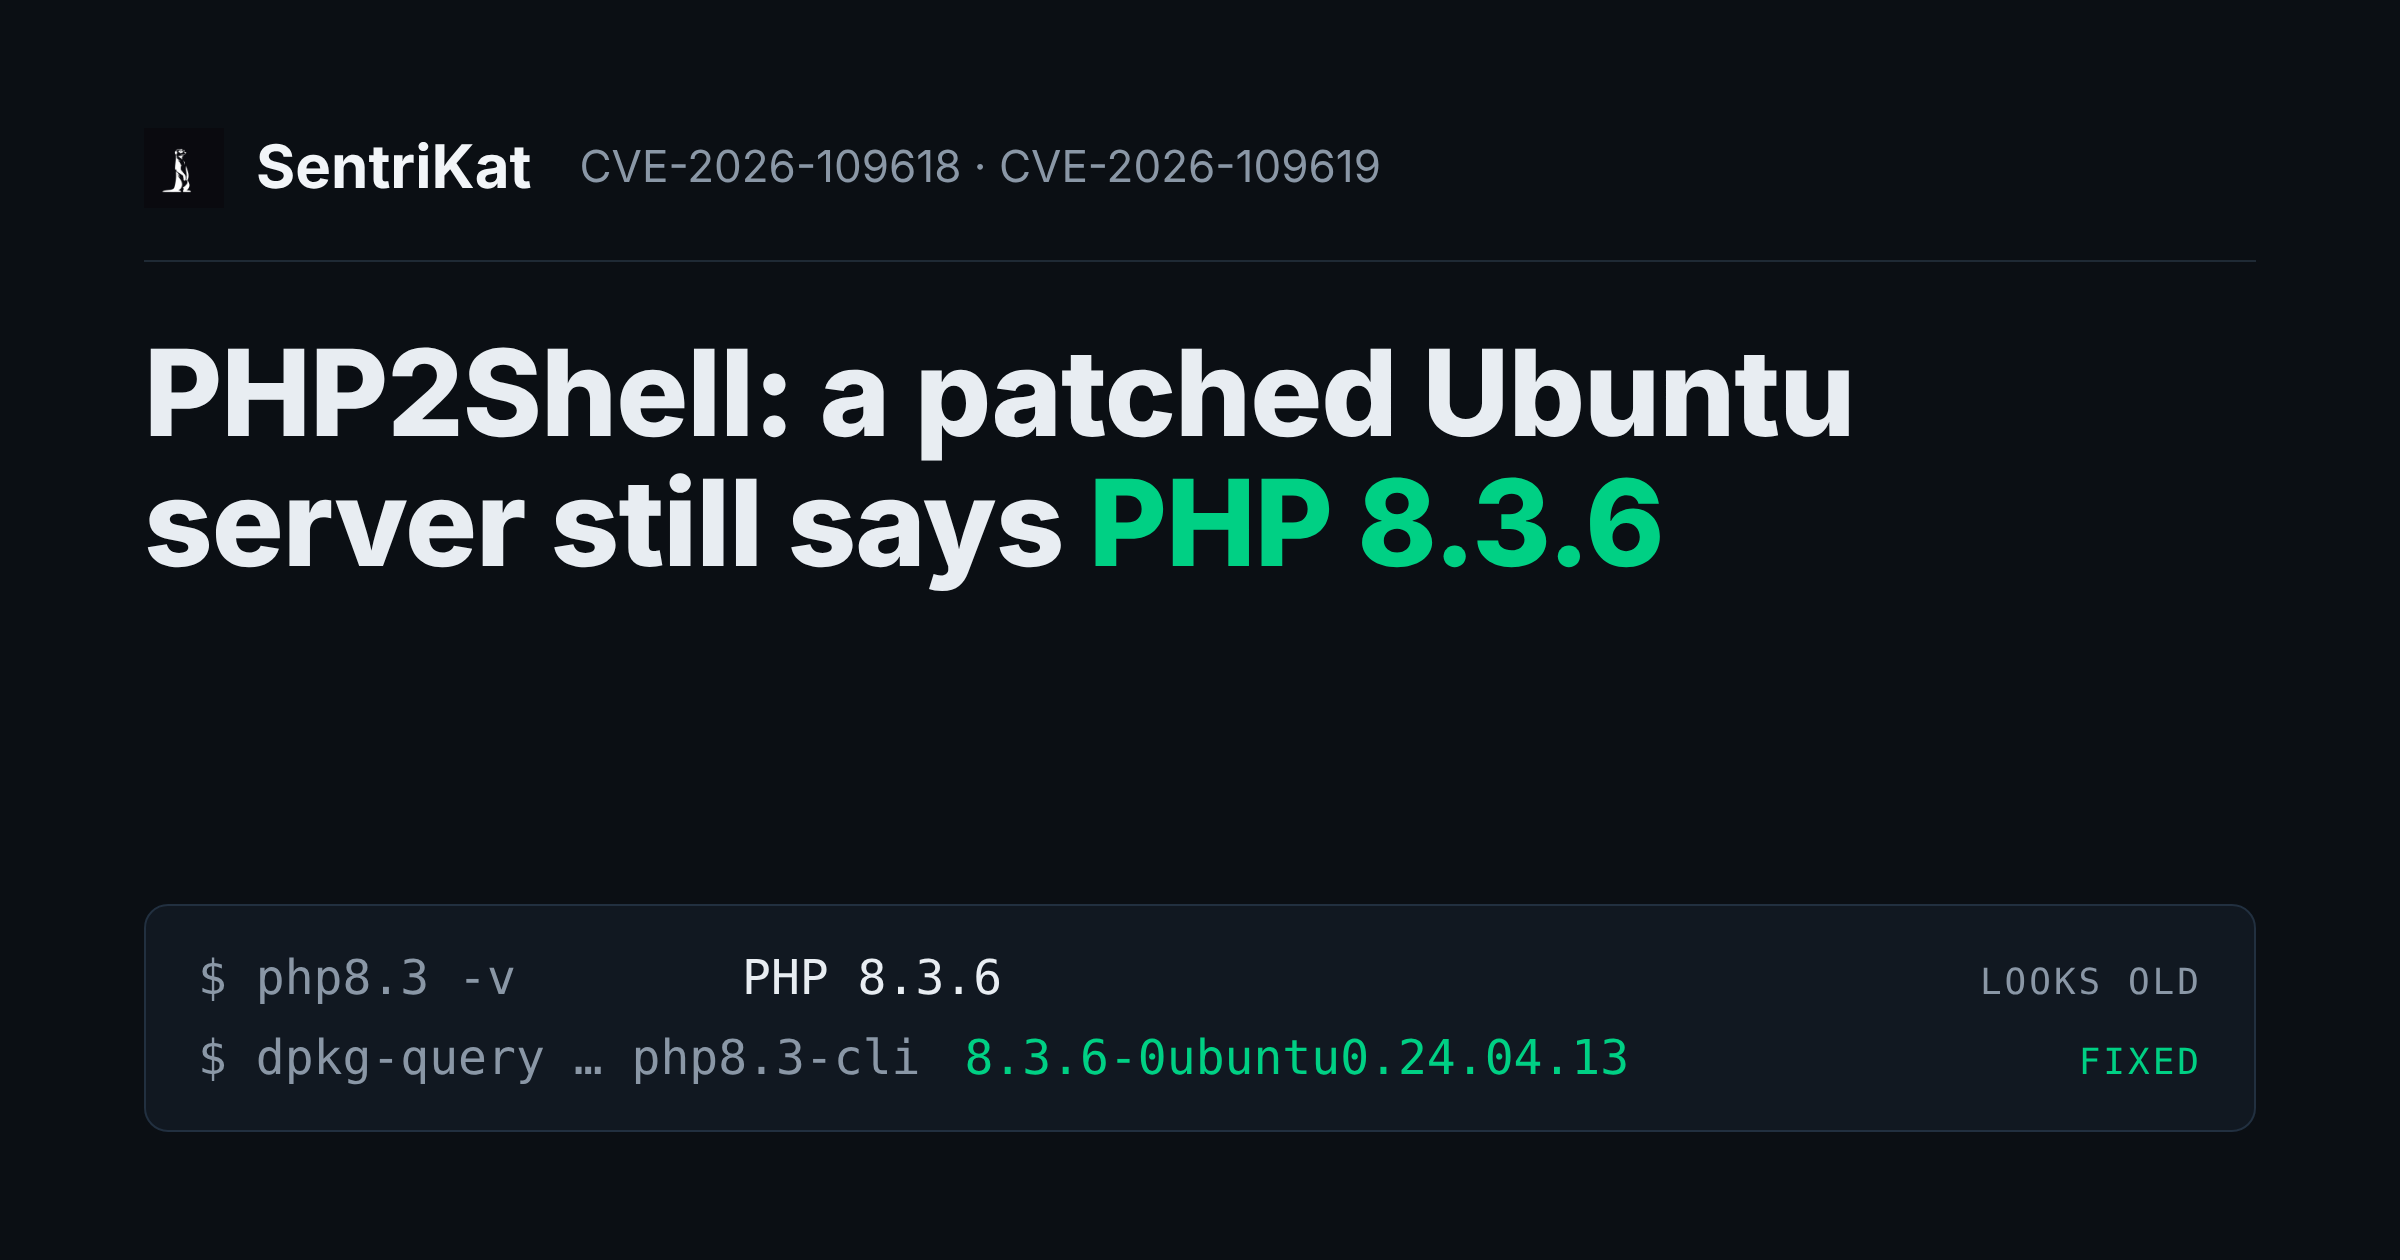
PHP2Shell: the hard part is not hearing about it, it's knowing which server to fix today

Two critical PHP flaws were officially published on 21 October 2026. A patched Ubuntu server still prints PHP 8.3.6, scanners that read NVD had nothing to match for almost three hours, and a small team has to get all of it right by hand. Hour by hour, what each source knew, and how to check a server properly.

Denis Sota · · 14 min read
NIS2 IT

NIS2 e gestione delle vulnerabilità: cosa chiedono davvero le misure di base dell'ACN

Inventari, piano di gestione delle vulnerabilità, aggiornamenti senza ritardo: cosa chiede la Determinazione ACN 379907/2025 e cosa preparare entro ottobre 2026.

· 8 min read
Five Days from Disclosure to Global Attack: The VMware vCenter Flaw That Could Not Wait NIS2

Five Days from Disclosure to Global Attack: The VMware vCenter Flaw That Could Not Wait

CVE-2026-59310 was exploited in 361 organizations across 47 countries within five days of Broadcom's advisory. Here is what that timeline means for your vulnerability management program, and why your current patch cadence probably would not have saved you.

· 7 min read
Your Email Server Is on the Attack List: Zimbra CVE-2026-73570 Joins CISA KEV NIS2

Your Email Server Is on the Attack List: Zimbra CVE-2026-73570 Joins CISA KEV

CVE-2026-73570 gives unauthenticated attackers remote code execution on Zimbra Collaboration Suite via a single SMTP request. CISA added it to the KEV catalog during the week of August 24. Here is what it does, who is exposed, and why NIS2-regulated organizations cannot wait on this one.

· 7 min read
Vulnerability management

Your scanner found 228 CVEs for Thunderbird. There are 1,830

The CPE dictionary has two names for Thunderbird, and most of the CVEs are under only one of them. Measured against the public NVD API, with the commands so you can repeat it.

· 3 min read
Vulnerability management

apt said the machine was patched. Two CVEs were waiting behind Ubuntu Pro

Our own scanner flagged two CVEs on gh on a fully updated Ubuntu 24.04 box. The fix had been published in February, in the ESM channel, where apt cannot see it. What we checked and what we did about it.

· 4 min read
Your AI coding agent ships an actively exploited vulnerability. Your scanner says it's clean Vulnerability management

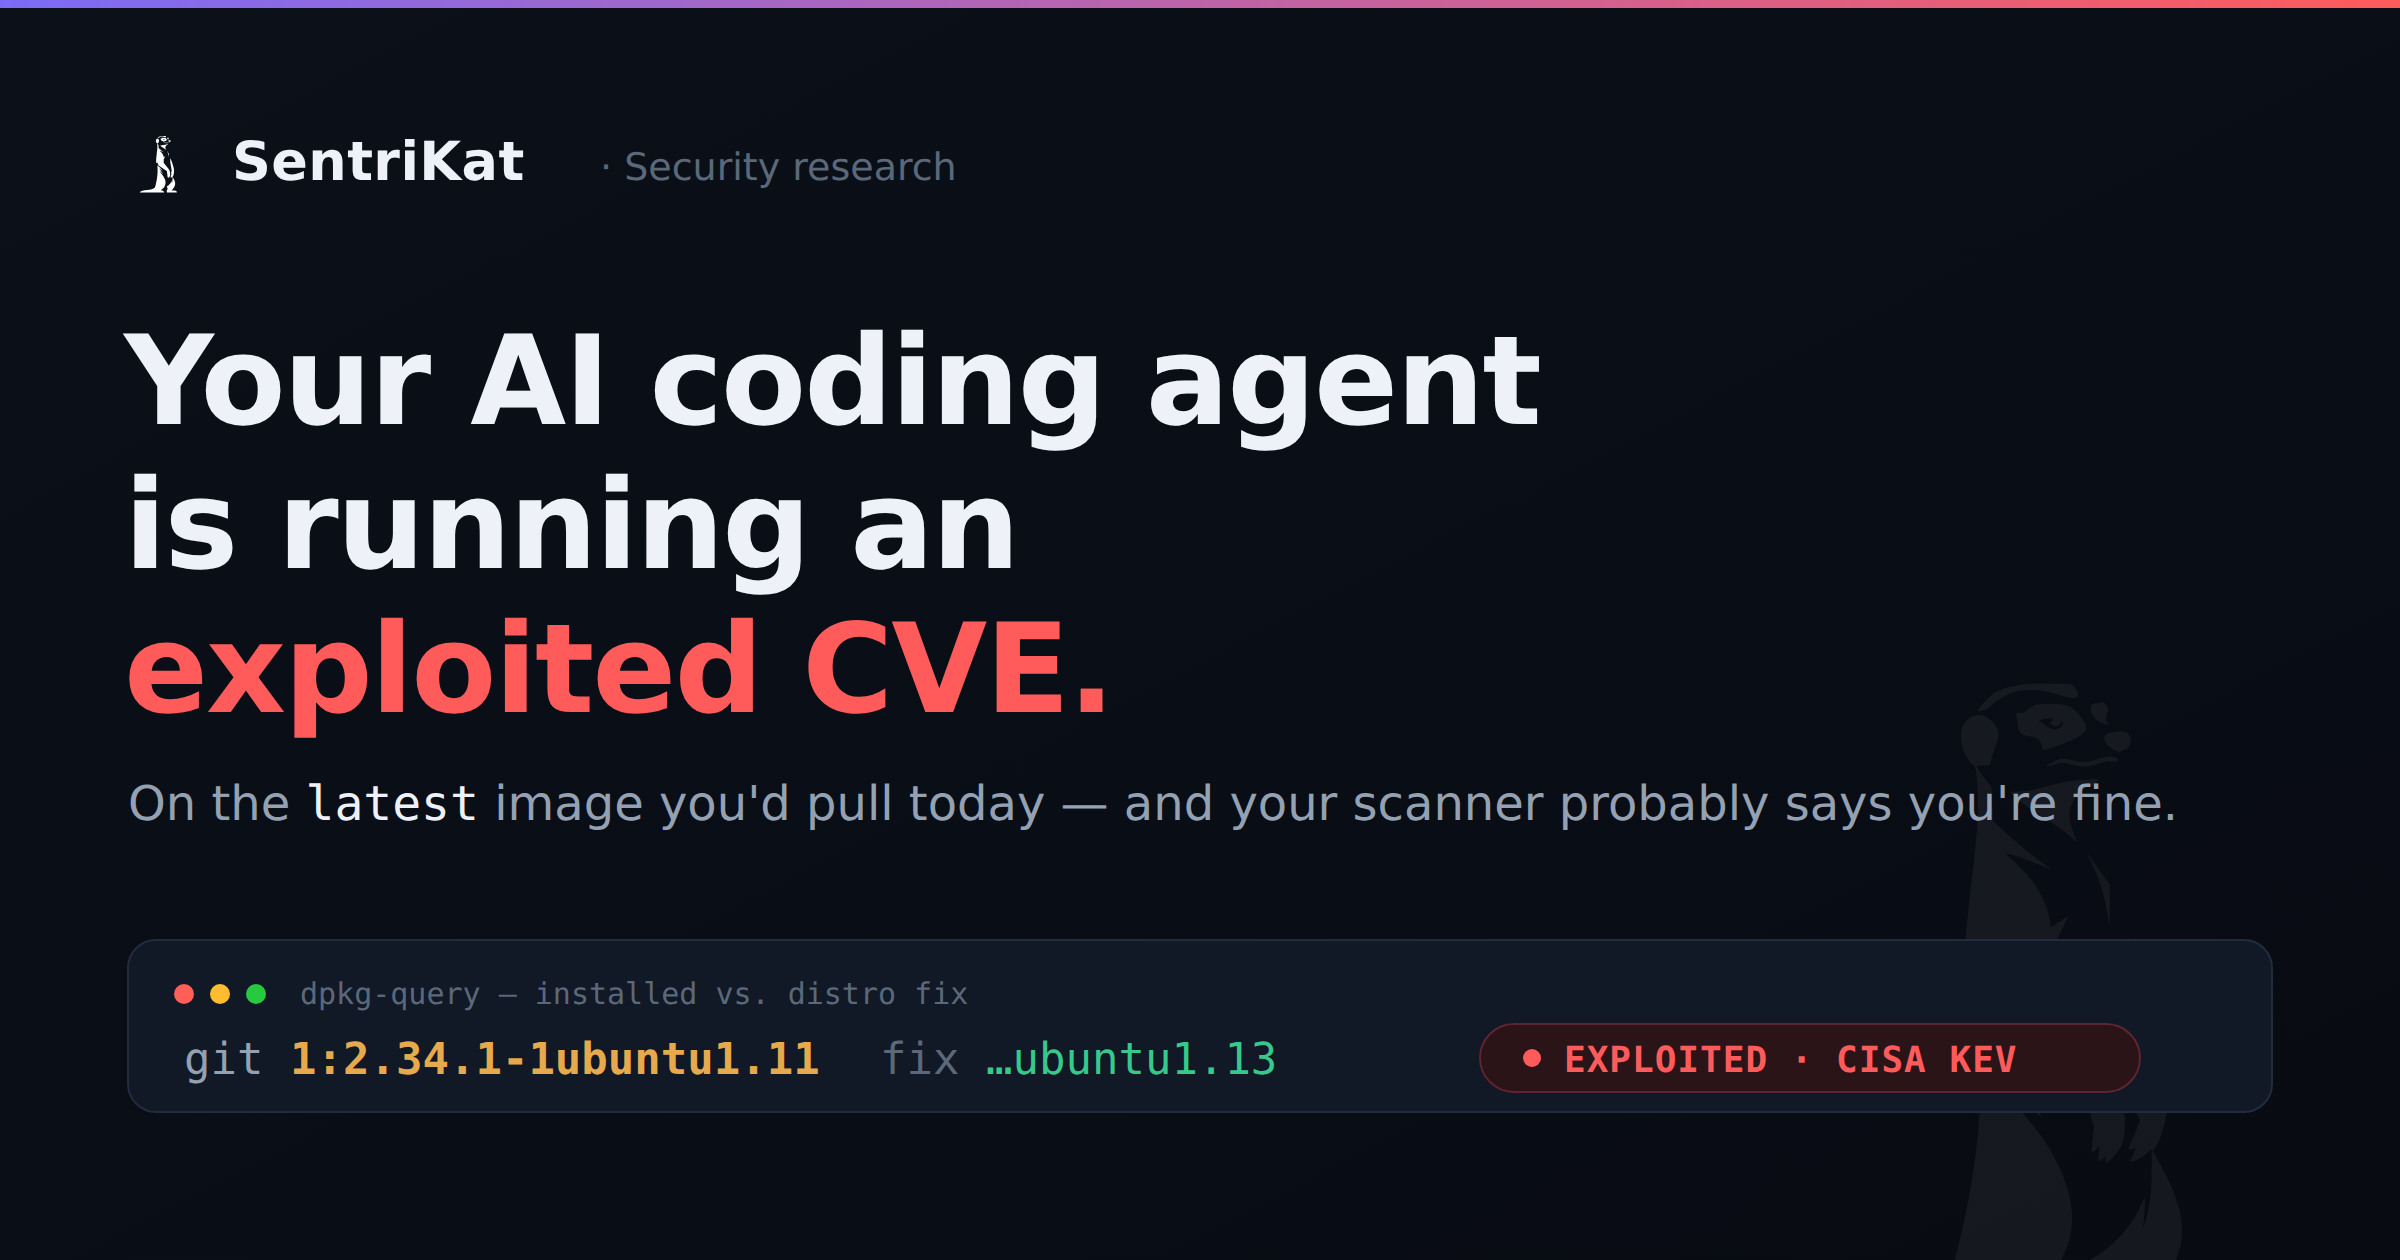
Your AI coding agent ships an actively exploited vulnerability. Your scanner says it's clean

I aimed our scanner at something almost nobody checks: the container images AI coding agents run inside. The current latest images ship a git flaw CISA lists as actively exploited, patched for months, and most scanners won't tell you. Here's why, and what to do about it.

· 13 min read
Guides

How We Benchmarked SentriKat Against Grype and Trivy

On a real production inventory, of the fixable OS-package CVEs that Grype and Trivy both agree on, SentriKat detects 97.3% (818 consensus CVEs), with fewer backport false positives. Here is the method, the numbers, and the parts still in triage.

· 5 min read
NIS2

AI-DLP for SentriKat: stop secrets leaking into ChatGPT, Copilot and Claude

SentriKat now offers an optional AI-DLP endpoint layer, powered by our open-source Contextia engine. Here's what it is, why it matters, and how to turn it on.

· 4 min read
DORA

DORA Pillar 5: Information & Intelligence Sharing, Voluntary, but a Maturity Signal

DORA's fifth pillar (Article 45) encourages financial entities to share cyber threat information and intelligence among trusted communities. It's voluntary, but participating is a clear sign of a mature resilience programme.

· 2 min read
DORA

DORA Pillar 2: ICT Incident Management & Reporting, The Clock and the Classification

DORA's second pillar (Articles 17–23) requires financial entities to detect, classify and report major ICT-related incidents to their competent authority on a defined timeline. Here's the practical shape of it.

· 3 min read
DORA

DORA Pillar 1: ICT Risk Management, What Financial Entities Need

DORA's first pillar (Articles 5–16) requires a board-owned ICT risk-management framework. Here's what that means in practice for banks, insurers, investment firms and their critical functions.

· 2 min read
DORA

DORA Vulnerability Management for Financial Services: A Practical Guide

DORA's ICT risk standard (EU 2024/1774, Art. 10) requires automated scans, at least weekly for critical or important functions. What to scan and record.

· 4 min read
NIS2

NIS2 Effectiveness Assessment (Article 21(2)(f)): Proving Your Controls Work

NIS2 Article 21(2)(f) requires policies to assess whether your risk-management measures are actually effective. Present, on paper, isn't the same as working, here's how to show the difference.

· 3 min read
Product

Launching our free public security scanner, what it checks and why we built it

A free, non-intrusive security posture scan for any public domain. Five categories, a 0–100 score, a PDF report, and zero data retention. Here's what's under the hood.

· 8 min read
NIS2

NIS2 MFA & Secured Communications (Article 21(2)(j)): The Highest-Impact Control

NIS2 Article 21(2)(j) calls for multi-factor authentication and secured communications. MFA is the single most effective control against the account compromise behind most breaches, here's how to get it right.

· 2 min read
NIS2

NIS2 Cryptography & Encryption (Article 21(2)(h)): Policy, Not Just Padlocks

NIS2 Article 21(2)(h) requires policies on cryptography and, where appropriate, encryption. The measure isn't 'turn on HTTPS', it's having a deliberate, documented approach to protecting data.

· 2 min read
NIS2

NIS2 Cyber Hygiene & Security Training (Article 21(2)(g)): The Human Layer

NIS2 Article 21(2)(g) requires basic cyber hygiene practices and security-awareness training. It's the cheapest, highest-leverage measure on the list, here's a practical baseline.

· 3 min read
Compliance & SBOM

Security posture update, HttpOnly sessions, nonce-based CSP, SBOM pipeline

A transparent write-up of the April 2026 security hardening on sentrikat.com and portal.sentrikat.com: what we changed, why it matters, and what's next.

· 6 min read
Compliance & SBOM

What's New in SentriKat, SBOM Export, Compliance Reports, and Remediation Workflows

Sprint 4 and Sprint 5 add SBOM export (CycloneDX, SPDX, STIX), signed gap-analysis reports for PCI-DSS, ISO 27001 and SOC 2, full remediation assignments with SLA tracking, and multi-tracker integration with Jira, GitHub, GitLab and YouTrack.

· 4 min read
NIS2

NIS2 Business Continuity & Backups (Article 21(2)(c)): Tested, Not Assumed

NIS2 Article 21(2)(c) requires backup management, disaster recovery and crisis management. The word that matters is 'tested', a backup you've never restored is a hope, not a control.

· 3 min read
NIS2

SentriKat Early Access Is Now Open, Free on the Plan You Choose, Limited Spots

We're opening SentriKat to 30 Cloud organizations for free, and the on-premises Community Edition to everyone: the plan you choose, with its own limits and features, no credit card, no time limit. Here's what you get and how to join.

· 4 min read
NIS2

NIS2 Incident Handling (Article 21(2)(b)): What You Actually Need

NIS2 requires essential and important entities to handle and report incidents on a strict timeline, 24-hour early warning, 72-hour notification, one-month final report. Here's what an incident-handling capability looks like in practice.

· 4 min read
NIS2

NIS2 Risk Analysis & Security Policies (Article 21(2)(a)): The Foundation

NIS2 Article 21(2)(a) requires a management-approved security policy and a maintained risk assessment. Here's what 'good enough' looks like for an essential or important entity, without the enterprise bureaucracy.

· 3 min read
NIS2 IT

Gestione delle Vulnerabilità per PMI: Guida Pratica alla Conformità NIS2

La direttiva NIS2 richiede la gestione delle vulnerabilità per le PMI europee. Scopri cosa serve, come implementarla senza budget enterprise, e come SentriKat automatizza la conformità.

· 4 min read
Vulnerability management

Vulnerability Management for MSPs: How to Scale Across Multiple Clients

One console for every client: isolated tenants, per-client reports, NIS2/DORA evidence per client and exploited-first alerts. Cloud or on-prem.

· 5 min read
Vulnerability management

Vulnerability Management in Air-Gapped Environments: A Practical Guide

How to manage vulnerabilities in air-gapped networks: signed offline updates, tracking what attackers exploit without internet access, and keeping data fresh.

· 6 min read
Vulnerability management

On-Premises vs Cloud Vulnerability Management: Why Data Sovereignty Matters

Should your vulnerability management tool be self-hosted or cloud-based? We compare on-premises and SaaS approaches for organizations that care about data sovereignty and GDPR compliance.

· 5 min read
NIS2

Why We Stopped Trusting a Single Vulnerability Database

SentriKat now fetches CVSS scores from 3 independent sources with automatic fallback. Here's why we built multi-source vulnerability intelligence and what the NVD backlog crisis means for your security posture.

· 4 min read
NIS2

What Is the ENISA European Vulnerability Database (EUVD)? A Practical Guide

EUVD is ENISA's European Vulnerability Database, live since May 2025 under NIS2. What it contains, how to search it, and how it relates to CVE IDs.

· 5 min read
Vulnerability management

EPSS vs CVSS: How to Actually Prioritize Vulnerabilities in 2026

CVSS scores alone don't tell you what to fix first. Learn how EPSS (Exploit Prediction Scoring System) and the CISA KEV catalog provide real-world exploit context for better vulnerability prioritization.

· 5 min read
NIS2

What Is the CISA KEV Catalog and Why Your Business Should Track It

The CISA Known Exploited Vulnerabilities catalog lists CVEs actively used in cyberattacks. Learn what KEV is, how it differs from the NVD, and why tracking it is essential for NIS2 and DORA compliance.

· 5 min read
NIS2

NIS2 Vulnerability Management: What European SMBs Need to Know in 2026

NIS2 requires vulnerability handling for essential and important entities across the EU. Learn what Article 21 demands, how to demonstrate compliance, and practical tools for SMBs.

· 5 min read

Get started with SentriKat

Cloud or on-premises vulnerability management focused on what's actively exploited.